When this happens, trade standards discard the algorithm and replace it with strong alternate options such because the SHA-2 household (SHA-256) or SHA-3. ITU Online IT Coaching covers these fundamentals in the context of Security+ so you have to use them appropriately on the job. Passwords should be hashed with salts and purpose-built password protection strategies, not saved as plain text. Use hashing for verification and integrity checks, not for confidentiality.
Technology Derived From A Decentralized Register Or Blockchain
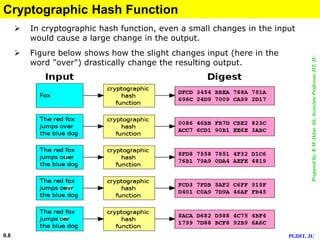
A widespread software for a hash-based PRF is for the era of symmetric keys. Message authentication is a mechanism or service used to confirm the integrity of a message. Message authentication assures that data acquired are precisely as sent (i.e., comprise no modification, insertion, deletion, or replay). In many cases, there is a requirement that the authentication mechanism assures that purported identification of the sender is valid. When a hash function is used to offer message authenti- cation, the hash operate value is also known as a message digest. When a hash perform is used to provide messageauthenti- cation, the hash operate value is also known as a message digest.
Security & Compliance
- Think about software downloads, configuration files, and backup archives.
- These features are also used in cryptocurrency to secure blockchain data and password safety.
- Not all hash algorithms are equally secure, and never all of them must be used for safety.
- The utility of hash operate is not secrecy; it is proving that knowledge stayed the identical.
- As a rule, a cryptographic hash function ought to be selected based on the safety goal, not just because it is acquainted or fast.
A general-purpose hash in a safety workflow can create a false sense of security, particularly when the attacker will get to decide on inputs. Hash verification is especially https://holidaynewsletters.com/what-is-ispmanager-overview-of-the-capabilities-and-advantages-of-the-control-panel.html useful when files move via multiple systems, mirrors, or staging environments. Every transfer creates one other probability for corruption or tampering. Real-world examples make the idea easier to know as a outcome of hashing is already built into frequent instruments and workflows.
Safe Communication Protocols
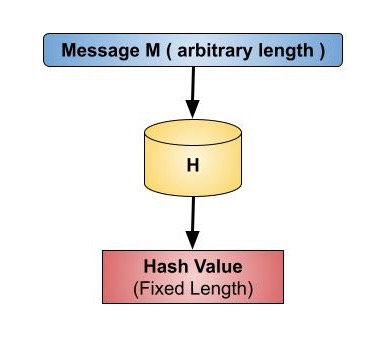
Regardless Of widespread utilization, Cryptographic Hash Algorithm 5 has demonstrated multiple vulnerabilities, together with collisions, the place two totally different inputs might generate the identical hash worth. This enables an attacker to create two separate messages with the identical hash and bypass security measures. Due to these vulnerabilities, Cryptographic Hash Algorithm 5 is considered a weak hash function and is being phased out in favor of extra robust hash strategies such as SHA-256. The Systematic Hash Algorithm (SHA) is a component of the SHA class of hash features, which was devised by the NSA and is extensively utilized in cryptography. SHA encompasses a number of numerous implementations; SHA-1, SHA-2, and SHA-3 are only some samples.
Sankalp Sharma
An algorithm is considered cryptographically broken when sensible collisions are discovered—that is, when two fully totally different enter information units generate the identical output hash. This irreversibility is key to their security, stopping attackers from retrieving sensitive info from hashes. It additionally helps the integrity verification process, as solely the original data can generate the identical hash, not vice versa. As a rule, a cryptographic hash function ought to be chosen based on the security aim, not simply because it is familiar or quick.
دیدگاهتان را بنویسید